Skip to content
Techzine Global
  • Home
  • Topstories
  • Topics
    • Analytics
    • Applications
    • Collaboration
    • Data Management
    • Devices
    • Devops
    • Infrastructure
    • Privacy & Compliance
    • Security
  • Insights
    • All Insights
    • Agentic AI
    • Analytics
    • Cloud ERP
    • Generative AI
    • IT in Retail
    • NIS2
    • RSAC 2025 Conference
    • Security Platforms
    • SentinelOne
  • More
    • Become a partner
    • About us
    • Contact us
    • Terms and conditions
    • Privacy Policy
  • Techzine Global
  • Techzine Netherlands
  • Techzine Belgium
  • Techzine TV
  • ICTMagazine Netherlands
  • ICTMagazine Belgium
Techzine » News » Security » More than 5,000 GitLab instances still vulnerable to account takeover
2 min Security

More than 5,000 GitLab instances still vulnerable to account takeover

Floris Hulshoff PolJanuary 25, 2024 10:23 amJanuary 25, 2024 10:23 am
More than 5,000 GitLab instances still vulnerable to account takeover

5,379 GitLab instances are still at risk. These instances may be affected by the recently discovered GitLab account vulnerability. ShadowServer research shows that accounts can still be taken over.

Recently, GitLab was affected by the critical vulnerability CVE-2023-7028. GitLab has since fixed this with a patch. However, ShadowServer research shows that many users have yet to install this patch. Potential risks include supply chain attacks, disclosure of proprietary code, API key leaks and other malicious activities.

Most vulnerable instances are in the U.S., totaling 964, followed by Germany (730), Russia (721), China (503), France (298), the UK (122), India (117) and Canada (99). However, no specific breaches have been reported at the time of writing.
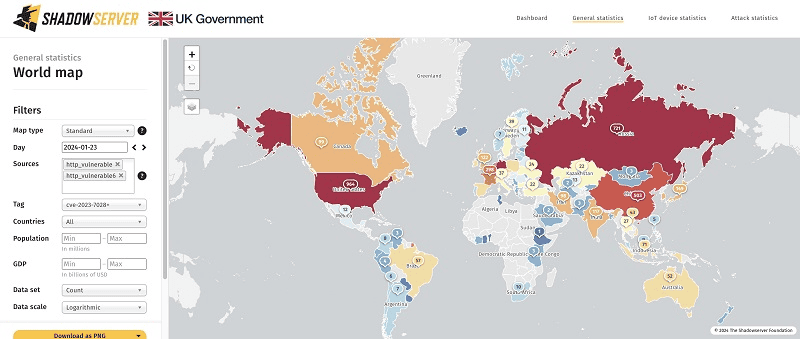
Een schermafbeelding van een website met een kaart van de wereld.

Features CVE-2023-7028

This vulnerability for GitLab instances allows attackers to perform a so-called zero-click attack to take control of instances.

This vulnerability allows hackers to send password reset emails for an attacked GitLab account to an email address they control. This way, they can then change the password and take over the account. However, when 2FA is enabled, this is blocked.

Fixes already released for some time

The problem occurs in GitLab Community and Enterprise Edition version 16.1 for 16.1.5, version 16.2 for 16.2.8, version 16.3 for 16.3.6, version 16.4 for 16.4.4, version 16.5 for 16.5.6, version 16.6 for 16.6.4 and version 16.7 for 16.7.2.

Two weeks ago, patches were released for versions 16.7.2, 16.5.6 and 16.6.4, as well as backporting patches for versions16.1.6, 16.2.9 and 16.3.7.

GitLab urges companies to still check their systems after implementing the updates for possible changes to their development environment, including source code and potentially modified files.

Also read: GitLab accounts vulnerable to takeover, patch available

Tags:

account takeover / CVE-2023-7028 / GitLab / instance

"*" indicates required fields

This field is for validation purposes and should be left unchanged.

Stay tuned, subscribe!

Nieuwsbrieven*

Related

Thousands of GitLab servers still unpatched against critical vulnerabilities

GitLab patches critical vulnerability that allows code execution

Large-scale GitLab scan reveals more than 17,000 leaked secrets

GitLab accounts vulnerable to takeover, patch available

Editor picks

Confluent opens pipe on Streamhouse data architecture

Confluent used its Current 2026 user/practicioner conference in San F...

vSphere Express: A return to an affordable VMware?

In addition to the usual improvements to VMware Cloud Foundation, Bro...

How Huawei is reinventing enterprise networking with AI

At Huawei Connect in Florence, Dennis Tossijn, ICT Network CTO at Hua...

Atlassian Jira is “for every team” but needs focus too

Dave Meyer, the Head of Product for Jira at Atlassian, has spent 15 y...

Techzine.tv

From edge nodes to 256-GPU clusters: HPE's private cloud explained

From edge nodes to 256-GPU clusters: HPE's private cloud explained

Microsoft reveals how it scales Kubernetes for OpenAI

Microsoft reveals how it scales Kubernetes for OpenAI

Why enterprises are running VMs on Kubernetes with Portworx

Why enterprises are running VMs on Kubernetes with Portworx

NetSuite Next and AI: what Oracle built behind the scenes

NetSuite Next and AI: what Oracle built behind the scenes

Read more on Security

Vulnerable cooling systems still accessible via the internet

Vulnerable cooling systems still accessible via the internet

Hundreds of Danfoss cooling systems remain accessible via the internet, even though security updates for the ...

Mels Dees 1 day ago
“Shoot first, ask questions later”: cybersecurity in the age of AI
Top story

“Shoot first, ask questions later”: cybersecurity in the age of AI

The average time between initial contact and full domain compromise has decreased dramatically over the past ...

Sander Almekinders 19 hours ago
Attackers use AntiFox AI penetration testing tool against AWS environments

Attackers use AntiFox AI penetration testing tool against AWS environments

Arctic Wolf has observed attackers deploying the open-source agent-based penetration testing platform AntiFox...

Berry Zwets 9 hours ago
Cisco tames Mythos, integrates it into AI Defense
Top story

Cisco tames Mythos, integrates it into AI Defense

Cisco is making AI Defense much more powerful by integrating Claude Mythos 5 into it. This doesn’t mean tha...

Sander Almekinders 2 days ago

Expert Talks

How physical security is becoming part of the IT business model

How physical security is becoming part of the IT business model

Physical security and IT have been technologically connected for year...

Why mobile device management doesn’t belong on personal devices

Why mobile device management doesn’t belong on personal devices

MDM was designed to control hardware the company owns. Pushed onto pe...

AI’s safety debate needs a clearer line

Generative AI can produce a convincing image in the time it takes to ...

Keeping up with F1: How high-performance storage powers live media production

At the Spa Grand Prix, Ethos had to turn a constant flow of footage i...

Tech calendar

Benelux Cyber Summit

November 24, 2026 Amsterdam

Celosphere 2026

December 2, 2026 Munich

Whitepapers

Experience Synology’s latest enterprise backup solution

Experience Synology’s latest enterprise backup solution

How do you ensure your company data is both secure and quickly recove...

How to choose the right Enterprise Linux platform?

How to choose the right Enterprise Linux platform?

"A Buyer's Guide to Enterprise Linux" comprehensively analyzes the mo...

Enhance your data protection strategy for 2025

The Data Protection Guide 2025 explores the essential strategies and...

Strengthen your cybersecurity with DNS best practices

The white paper "DNS Best Practices" by Infoblox presents essential g...

Techzine Global

Techzine focusses on IT professionals and business decision makers by publishing the latest IT news and background stories. The goal is to help IT professionals get acquainted with new innovative products and services, but also to offer in-depth information to help them understand products and services better.

Follow us

Twitter
LinkedIn
YouTube

© 2026 Dolphin Publications B.V.
All rights reserved.

Techzine Service

  • Become a partner
  • Advertising
  • About Us
  • Contact
  • Terms & Conditions
  • Privacy Statement