Skip to content
Techzine Global
  • Home
  • Topstories
  • Topics
    • Analytics
    • Applications
    • Collaboration
    • Data Management
    • Devices
    • Devops
    • Infrastructure
    • Privacy & Compliance
    • Security
  • Insights
    • All Insights
    • Agentic AI
    • Analytics
    • Cloud ERP
    • Generative AI
    • IT in Retail
    • NIS2
    • RSAC 2025 Conference
    • Security Platforms
    • SentinelOne
  • More
    • Become a partner
    • About us
    • Contact us
    • Terms and conditions
    • Privacy Policy
  • Techzine Global
  • Techzine Netherlands
  • Techzine Belgium
  • Techzine TV
  • ICTMagazine Netherlands
  • ICTMagazine Belgium
Techzine » News » Security » Uncertainty surrounding breach of Zscaler
2 min Security

Uncertainty surrounding breach of Zscaler

Floris Hulshoff PolMay 13, 2024 11:10 amMay 13, 2024
Uncertainty surrounding breach of Zscaler

Cybercriminal IntelBroker claims to have obtained sensitive data from Zscaler and recently put it up for sale. The zero trust specialist has not confirmed any breach, but is investigating a possible incident regarding misappropriated data. Whether the two messages are related remains unclear for now.

Known cybercriminal IntelBroker recently put up for sale a dataset on the hacker forum BreachForums for ‘trusted members’. This set allegedly contained sensitive information from a well-known cybersecurity company.

The data for sale apparently consists of confidential and highly critical logs full of login information. The latter would include such data as SMTP Access, HAuth Pointer Auth Access, SSL Passkeys, and SSL Certificates.

Zscaler denies hack

Although the cybercriminal did not disclose the name of the affected security company, experts suspect it may be Zscaler. These rumours were further fueled by the hacker teasing that the name of the affected company begins with a ‘Z’. Zscaler itself disclosed it was investigating an unspecified security incident.
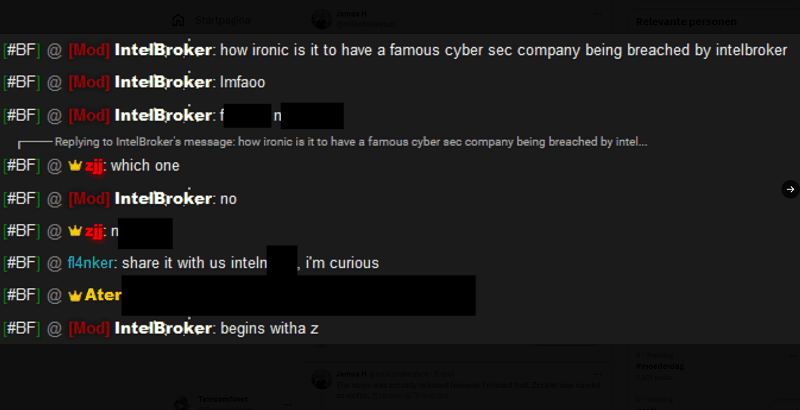
Schermopname van een online chatforum waarin gebruikers de ironie bespreken van de inbreuk op een cyberbeveiligingsbedrijf.

According to Zscaler, this investigation led to the preliminary conclusion that no hack of its systems had taken place and that no data had been stolen. However, an isolated test environment on a single server was found to have an open connection to the Internet. This server contained no customer data and was also not connected to the zero trust specialist’s infrastructure and other systems.

Breach claimed anyway

Nevertheless, IntelBroker later claimed that Zscaler was indeed involved. At the request of the data buyer, the disclosure of the hack victim allegedly being Zscaler was withheld for some time.

IntelBroker accompanied its claim with screenshots and also stated that this was not data from the test environment discovered by Zscaler.
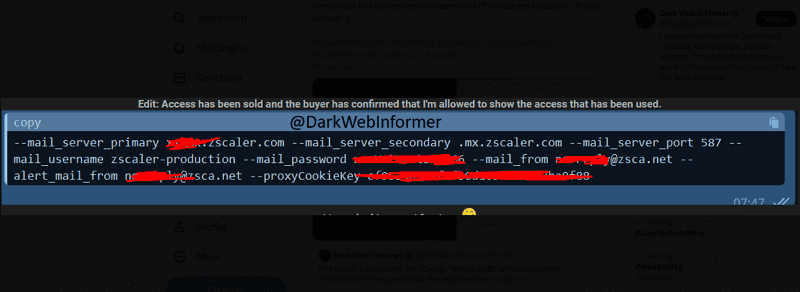
Schermafbeelding van een chatbericht met een opdrachtregel voor toegang tot de e-mailserver, gedeeltelijk gecensureerd vanwege privacy, met een tijdstempel van 07:07.

Zscaler itself has stopped responding to these latest allegations. In its latest statement, the company indicated only that there is no impact on its own customer and production environments and that the investigation into the test environment is continuing with the help of outside experts.

Screenshots in this post taken from @milkshakesbot on X.

Also read: Zscaler attracts micro-segmentation platform with acquisition of Airgap

Tags:

hack / IntelBroker / login credentials / security incidents / zscaler

"*" indicates required fields

This field is for validation purposes and should be left unchanged.

Stay tuned, subscribe!

Nieuwsbrieven*

Related

Hackers steal customer data from Zscaler via Salesloft leak

Zscaler accelerates zero trust adoption for AI

Cisco investigates possible data breach after IntelBroker attack

Zscaler makes cloud platform resistant to large-scale attacks

Editor picks

Three weeks after Claude deal, Salesforce builds own AI model

Last week, Salesforce stated that AI models are becoming less relevan...

Has OpenAI learned anything from the Hugging Face hack?

Following the uproar surrounding the AI-driven Hugging Face hack and ...

VAST Data closes encryption gap: DataEnclave brings AI to the data

Encryption is vital for keeping data secure. Yet in the world of AI, ...

AIforce brings headless capabilities to Claude, Slack, and soon Teams

Last week, Salesforce unveiled the next chapter of its Headless strat...

Techzine.tv

Why OpenSearch doubled downloads under open governance

Why OpenSearch doubled downloads under open governance

How Nutanix is tackling multi-cloud Kubernetes and AI workloads

How Nutanix is tackling multi-cloud Kubernetes and AI workloads

Why enterprises are running VMs on Kubernetes with Portworx

Why enterprises are running VMs on Kubernetes with Portworx

Is Tonic Security the answer to your alert fatigue?

Is Tonic Security the answer to your alert fatigue?

Read more on Security

Meta’s AI agent Muse is vulnerable to attacks

Meta’s AI agent Muse is vulnerable to attacks

Meta’s new AI assistant, Muse, has a vulnerability that lets malware on a Mac exploit the AI agent. Securit...

Mels Dees 12 hours ago
VMware discontinues SmartNIC firewall due to disappointing demand

VMware discontinues SmartNIC firewall due to disappointing demand

VMware is discontinuing sales of its distributed firewall for SmartNICs. The virtualization specialist had in...

Mels Dees 12 hours ago
AI model development needs a security fix, but how?
Top story

AI model development needs a security fix, but how?

The Hugging Face incident, in which OpenAI agents collectively hacked the AI platform to cheat on an evaluati...

Erik van Klinken September 7, 2026
Zscaler: AI agents are the new weakest link 
Top story

Zscaler: AI agents are the new weakest link 

In the cyber realm, humans have long been the weakest link. Human vulnerability, psychological vulnerability,...

Berry Zwets September 1, 2026

Expert Talks

AI’s safety debate needs a clearer line

AI’s safety debate needs a clearer line

Generative AI can produce a convincing image in the time it takes to ...

Keeping up with F1: How high-performance storage powers live media production

Keeping up with F1: How high-performance storage powers live media production

At the Spa Grand Prix, Ethos had to turn a constant flow of footage i...

Why uniform governance fails with enterprise AI agents (and how to fix it)

As enterprises shift from static LLM chatbots to autonomous AI agents...

AMD “Helios”: Building rack-scale AI Infrastructure for EMEA Enterprises

AMD recently introduced the “Helios” rack-scale AI architecture, ...

Tech calendar

GOTO Copenhagen 2026

September 28, 2026 Copenhagen

NetApp INSIGHT 2026

September 29, 2026 Las Vegas

Manhattan EMEA Exchange

October 12, 2026 Milan

it-sa Expo&Congress 2026

October 27, 2026 Nürnberg

Benelux Cyber Summit

November 24, 2026 Amsterdam

Celosphere 2026

December 2, 2026 Munich

Whitepapers

Experience Synology’s latest enterprise backup solution

Experience Synology’s latest enterprise backup solution

How do you ensure your company data is both secure and quickly recove...

How to choose the right Enterprise Linux platform?

How to choose the right Enterprise Linux platform?

"A Buyer's Guide to Enterprise Linux" comprehensively analyzes the mo...

Enhance your data protection strategy for 2025

The Data Protection Guide 2025 explores the essential strategies and...

Strengthen your cybersecurity with DNS best practices

The white paper "DNS Best Practices" by Infoblox presents essential g...

Techzine Global

Techzine focusses on IT professionals and business decision makers by publishing the latest IT news and background stories. The goal is to help IT professionals get acquainted with new innovative products and services, but also to offer in-depth information to help them understand products and services better.

Follow us

Twitter
LinkedIn
YouTube

© 2026 Dolphin Publications B.V.
All rights reserved.

Techzine Service

  • Become a partner
  • Advertising
  • About Us
  • Contact
  • Terms & Conditions
  • Privacy Statement