HP has identified several cybercriminal campaigns using its proprietary Sure Click technology within Wolf Security. The payloads were able to strike within a micro-VM, allowing HP to record the behavior and tactics behind the malware.
A fake cryptocurrency trading bot, phishing campaigns, and a so-called penetration testing tool were detected via HP Sure Click. In the first case, the attackers chose to build a website that gave the impression the product behind it was growing rapidly. This was suggested, among other things, by the fact that a Windows version was available and a macOS variant was set to arrive soon.
The so-called Needle Stealer was embedded in the malware that purported to automate crypto trading. However, it was not hidden in the .exe file but was delivered via a .dll file bundled with a Microsoft-signed program. The crypto wallet that users saw in their browser was a counterfeit copy of the genuine version.
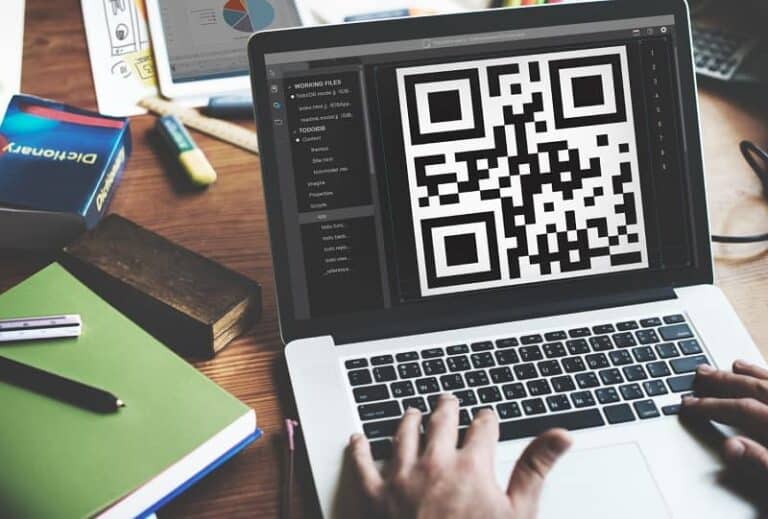
QR code in PDF invoice
In another campaign, a PDF purporting to be an invoice served as the attack vector. The QR code visible in the document made using a smartphone seem appealing. The result was bypassed endpoint security and a fake login page that also used a CAPTCHA to thwart automated scans. A spoofed Microsoft login page then helped the criminals obtain the victim’s credentials.
The third campaign contained Phantom Stealer and promoted a penetration testing tool, software used to verify the security of software, infrastructure, or authentication processes. A PowerShell script delivered Phantom Stealer. A loader integrated into the PowerShell script was called Phantom Gate. This loader retrieves the payload and executes it within a legitimate .NET Framework process. HP suspects that both pieces of malware share the same origin and serve as a ready-made solution for cybercriminals.
More difficult to detect
Cybercriminals seem all too aware of defenders’ efforts to detect their actions early on. The attackers’ response, therefore, is to appear as legitimate as possible and switch endpoints when necessary. Furthermore, automated scanners are so detrimental to malware distribution that attackers must verify whether potential victims are actually at the controls, and not a defensive agent.
This means that organizations must rely far less on detection and automated defensive layers. Attack campaigns rarely follow predictable paths that reveal clear signs of malicious intent. The nature of deception runs deeper and extends beyond a single endpoint. HP Sure Click offers a different approach than standard EDR solutions by running malicious programs, which often arrive via email, in a secure sandbox. This yields a diverse range of detections involving exploits targeting PDFs, login pages, and QR codes.
See also: New attack technique freezes endpoint security via Windows feature