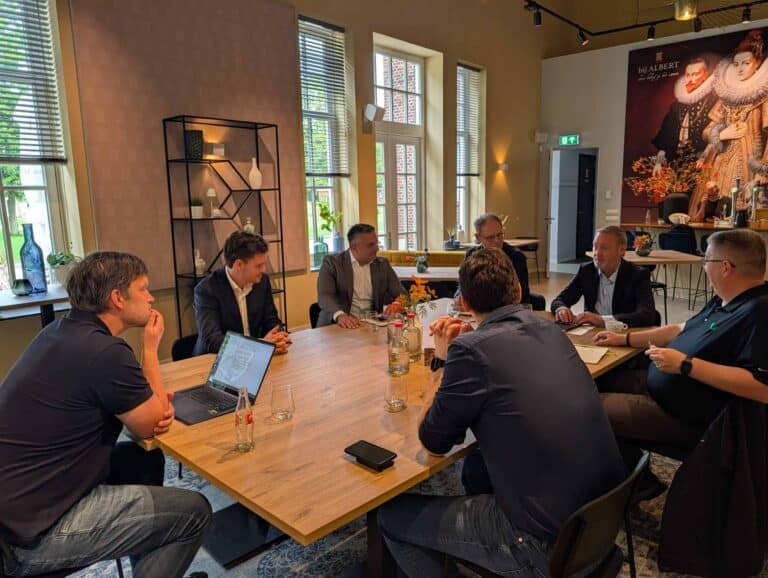
The traditional approach to data security no longer works today. In the past, sensitive corporate data was securely anchored behind trusted business applications and static firewalls. However, autonomous AI agents now tirelessly and rapidly scour corporate networks in search of information. How do you maintain control when these invisible digital workers constantly push the boundaries of your data environment, link files together, and make decisions at machine speed? We discuss this in an in-depth roundtable with Dell Technologies, Fox-IT, Klarrio, Everpure, Thales, and Veeam.
For years, especially compared with today, cybersecurity was relatively straightforward. You built a digital castle wall around your infrastructure and trusted that your data was safe as long as the gate remained closed. That model began to show cracks with the shift to the cloud and hybrid work, but the rise of generative AI and autonomous agents has fundamentally changed the playing field itself. Today, securing data in an AI-driven landscape requires a radically different approach than the one we have been accustomed to over the past few decades.
In this first part of a two-part series on data security, experts examine the true impact of AI on IT’s “crown jewels” as well as why this requires companies to rethink their approach to data security today.
Explosion of complexity
It quickly becomes apparent early in the discussion that experts are seeing growing interest in data. This is because data drives AI, offers value, and can essentially be translated into monetary terms. Modern organizations are actively seeking to collect data and derive insights from it. Consequently, corporate data environments are expanding rapidly in various ways. There is more data than ever; spanning diverse types and requiring a range of systems.
Securing it properly using the traditional security model is no longer feasible. In fact, Werner Vermeylen of Klarrio sees complexity increasing exponentially. According to him, the security landscape has rapidly transformed into an extremely dynamic model. “Whereas you used to have a straightforward data store containing human identities and clear, one-off access controls, you now have AI agents, external APIs, and endless data streams and log files everywhere, continuously unlocking information,” Vermeylen explains.
In practice, he sees AI essentially acting as a ruthless magnifying glass for existing IT problems. “Many companies possess vast amounts of legacy data—data whose exact content they don’t even know, or that was simply never classified or annotated. When you then unleash an AI agent on that data—one allowed to scrape everything and draw connections—you rapidly create unmanageable risk.”
Seal everything up tight
The promise of AI lies in its increased efficiency; a promise that is certainly being fulfilled. From a security perspective, however, that efficiency creates a blind spot. Organizations are grappling with how to maintain control over systems that make autonomous decisions and cut across all data silos. This operational shift compels IT departments to take a fundamentally different approach to access management. While reliance on the good intentions of internal users may have sufficed in the past, absolute vigilance is now required.
Dick Vonk of Dell Technologies takes a firm stance: defense strategies must return to a strict regime. “You really need to treat autonomous AI agents exactly like human employees, but with the brakes applied,” he argues. “That means tightly and meticulously locking down their permissions within your own environment. Zero trust, even within your own infrastructure. If you don’t, they’ll run wild in every direction and start intervening everywhere.”
To avoid losing control, Vonk also warns against over-reliance on external, public AI models, noting that data ownership becomes a grey area in such scenarios. He believes the safest path is autonomy: “Bring the AI engine to your own data and keep development in-house. That’s the only way to ensure you know who has access to your files; that you have a concrete recovery point if something goes wrong; and that prevent your business data from ending up as training material in third-party systems.”
An agent’s curiosity
Edwin Weijdema of Veeam agrees on the need for strict parameters. However, he points out a behavioral distinction between the actions of AI and those of humans. According to him, many companies underestimate the fact that an AI agent behaves completely differently on the network than a flesh-and-blood employee. “A regular employee has a defined role and access to a limited set of resources. This human employee follows a logical process, opens only the specific files needed for their daily work, and then logs off.”
However, an AI agent is designed to seek out connections, making it inherently curious. “The agent will rapidly test things out in the background,” Weijdema continues. “It constantly knocks on every digital door within the infrastructure, asking: ‘Do I have access to this, too?’” Because these systems can instantly establish connections (such as within log files) that would remain invisible to humans, traditional security measures are insufficient. Weijdema therefore advocates for the introduction of a deep, contextual layer, known as a ‘trust layer.’ This layer sits directly on top of the data, continuously verifying the type of data an agent is attempting to process. While this represents an additional step, given the billions of files within organizations, it can help to better protect sensitive information, among other things.
Monitoring at machine speed and dynamic permissions
LIdentity and Access Management is logically linked to the implementation of data security. After all, without IAM, data security is left in the dark regarding who is requesting data; conversely, without data security, IAM cannot gauge the sensitivity of the data lying behind the access point. However, there are doubts about the effectiveness of traditional IAM. Floris Dankaart (Fox-IT) observes that assigning fixed roles and permissions simply no longer scales in an AI landscape. He points to the unprecedented complexity of the permissions structures that IT administrators now face. “You are dealing with an AI agent that, depending entirely on the context in which it is operating at any given moment, assumes different roles and consequently holds widely varying permissions for diverse datasets.”
In this dynamic environment, a strong gatekeeper or a robust firewall at the front door offers insufficient protection. “Even if you have perfectly secured the front end through prevention, there is always a significant risk of exploitation,” warns Dankaart. This can range from malicious actors executing prompt injections to undiscovered vulnerabilities hidden deep within the AI model itself. That’s why security teams need to shift from relying solely on prevention to continuous, real-time monitoring, he says. “If an agent goes rogue or steps out of bounds at machine speed, how do you ensure you can correct it quickly? Can you rapidly disconnect it from the network or disable its identity? That entire picture is relevant when discussing data security.”
Data as its own gatekeeper
A consensus is emerging as a result of the explosion in shifting identities and bypassable entry points. As the traditional network perimeter and corporate applications lose their hold, the primary line of defense must shift to the very core of the enterprise. Marco Bal (Everpure) views this as a necessary and profoundly transformative architectural shift. It used to be simple: the application managed the data and determined, based on strict rules, who could access it. Today, however, that approach is no longer tenable.
In this sense, the primary focus and concern must truly be on the data itself, independent of the platform on which it runs, now that the application is no longer the sole gatekeeper. In this new setup, according to Bal, data must be capable of communicating its own context; it needs to become “self-describing.” This is achieved by embedding aspects such as access rights directly into the information via metadata. “That way, the network always knows precisely whether it is dealing with, for instance, privacy-sensitive medical records or financial transactions,” Bal states. Determining whether an action is safe no longer depends on a specific application; instead, the data effectively protects itself. This protection remains intact regardless of whether an autonomous agent or a human employee is working with the data.
Fighting fire with fire
Despite the immense complexity and new risks accompanying the introduction of AI, the market refuses to resign itself to a doomsday scenario. Ilkay Kahraman of Thales, for instance, introduces a necessary sense of nuance and optimism. He puts the existential threat into perspective by stripping the technology back to basics: ultimately, at its core, an AI agent is simply yet another digital identity on a network. The crucial difference, however, is that this entity operates at unprecedented speed, possesses immense processing power, and can execute tasks seamlessly in parallel.
“We certainly need to define and audit the boundaries of that specific identity, and what it is permitted to do within the infrastructure, with extreme strictness,” says Kahraman. Yet, the defending party need not adopt a position of powerlessness. Kahraman emphasizes that we should actually leverage AI’s immense computing power and speed as the ultimate weapon in our favor. “We really have no other choice. After all, our adversaries, the cybercriminals targeting our data, are already making full use of this technology to scan networks automatically.” To counter that lightning-fast, automated AI threat from the outside, organizations have no option but to fight fire with fire. “You simply have to counter it with something equivalent, AI-driven monitoring and detection from within, to maintain control.”
This was the first part of a two-part series on data security. In the next article, we’ll delve deeper into secure hardware, post-quantum cryptography, and getting your database in order.